The following article is excerpted from “Advanced Strategic Technologies” and was written by the Yuanwang Think tank, “Foresight”.
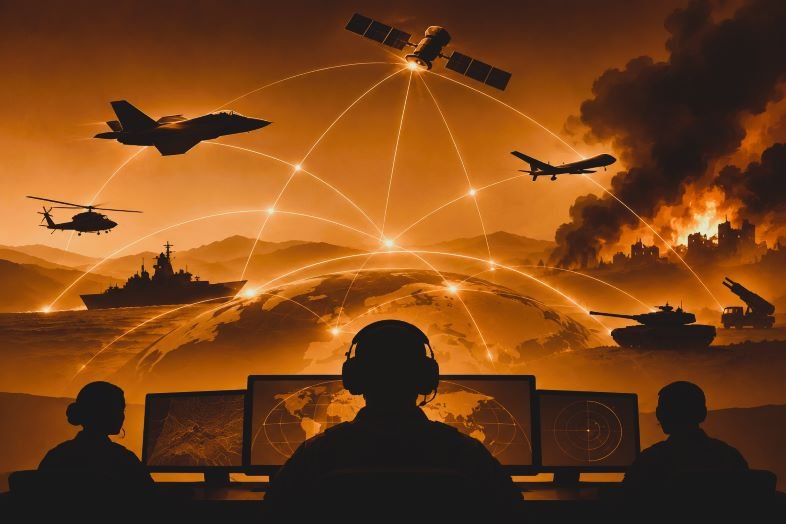
Introduction: Connecting every sensor and weapons platform across the land, sea, air, space and cyber domains to enable “any sensor to guide any shooter” is the essence of JADC2, the U.S. military’s Joint All-Domain Command and Control concept. After evolving from a paper strategy and a collection of service-specific programs to a system tested in combat operations in the Middle East, how capable is this much-anticipated command architecture, and what institutional and technological challenges remain unresolved?
Against the backdrop of great-power competition, the U.S. military has concluded that traditional C4ISR command-and-control systems are no longer adequate for anti-access/area-denial environments. It has therefore developed JADC2, later upgraded to CJADC2, or Combined Joint All-Domain Command and Control, which brings allied systems into the network.
JADC2 is not a new piece of equipment but a revolution in the command-and-control paradigm. It shifts the focus from systems to data, with the aim of compressing the OODA loop and securing a decision-making advantage.
1. A Paradigm Shift: What Is JADC2?
Traditional command-and-control systems were built by first developing a range of independent systems, with each system generating and managing its own data. Service-specific systems operated in isolation, creating what are commonly known as “information stovepipes.” Cross-domain coordination required extensive manual conversion and gateway translation, and kill chains often took hours to complete.
JADC2 turns that logic on its head. Instead of starting with separate systems, it creates a unified data environment into which different platforms connect as data producers and consumers. Its top-level capability can be summed up as a three-step cycle: sense, understand and act.
- Sense: Aggregate data from multiple sources, including satellites, aircraft, ships and ground-based radars.
- Understand: Use artificial intelligence and data fabrics to fuse the information and generate a common operating picture.
- Act: Intelligently match sensors with strike platforms to coordinate cross-domain fires, then feed the results of those strikes back into the system for further refinement.
The architecture is supported by the VAULTIS data-governance framework, which requires data to be visible, accessible, understandable, linked, trustworthy, interoperable and secure. Its underlying infrastructure relies on the Joint Warfighting Cloud Capability, or JWCC, a multivendor military cloud system. At the security layer, it broadly adopts a zero-trust architecture.
In 2023, the addition of the word “Combined” transformed JADC2 into CJADC2, bringing allied sensors and weapons platforms into the broader network. The Mission Partner Environment, or MPE, provides the technical foundation for sharing data with mission partners.
2. Five Services, Five Separate Paths
JADC2 is not a single overarching program. Instead, its implementation has been divided among the five U.S. military services through a series of signature initiatives. This has been a source of innovation, but it also represents the architecture’s greatest institutional vulnerability.
1. The Air Force’s Advanced Battle Management System
The Advanced Battle Management System, or ABMS, was launched first and has generated the most controversy. It was initially intended to replace the E-3 airborne early-warning aircraft and the E-8C reconnaissance aircraft. Operating through a “system of systems” model, it has used multiple On-Ramp exercises to test cross-domain data flows.
But unclear requirements and repeated congressional budget cuts have forced the vision to shrink. Long-standing problems, including the lack of full compatibility between the F-22 and F-35 data links, remain unresolved.
2. The Army’s Project Convergence
Project Convergence follows an “experiment-as-development” model, using annual field exercises to drive successive iterations. In its early stages, the project produced a widely cited 20-second sensor-to-shooter kill-chain cycle under controlled test conditions.
That result, however, was achieved in an ideal, interference-free environment and cannot be directly applied to an actual battlefield.
3. The Navy’s Project Overmatch
Project Overmatch is closely tied to the Navy’s Distributed Maritime Operations concept. It is designed for operations across vast maritime spaces and focuses on networking ships and unmanned platforms.
Very little information about the program has been made public. A Government Accountability Office audit has noted that data exchange between Project Overmatch and the Air Force’s ABMS remains limited in practice.
4. The Marine Corps’ Project Dynamis
Project Dynamis was launched last and is geared toward Expeditionary Advanced Base Operations, or EABO. Constrained by budget limitations, it relies heavily on capabilities developed by the Navy and Air Force, advancing through a lighter and more modular approach.
5. Space Force C4ISR Support
The Space Force provides the communications and early-warning foundation through the Proliferated Warfighter Space Architecture, or PWSA, and Starshield. Its extensive use of commercial space capabilities, however, also creates new risks stemming from dependence on commercial suppliers.
The services are building their systems separately, while the JADC2 cross-functional team responsible for coordination has only advisory authority and no power to issue binding orders. It therefore cannot impose common data standards across the services, embedding institutional weaknesses in the “joint” concept from the very beginning.
3. From Exercises to Combat: A Major Gap Between Theory and Reality
A series of On-Ramp events, Project Convergence exercises and Large Scale Exercises have shown that JADC2 can connect sensors to shooters across multiple domains in an ideal environment. But combat operations in the Middle East from 2024 to 2026 have exposed the limits of that experimental success.
In combat operations in the region, JADC2 used capabilities associated with Palantir’s AIP and the Maven program to fuse intelligence from multiple sources, prioritize targets and assist in generating strike plans. Yet the time required to complete the kill chain in combat was approximately 12 minutes, dozens of times longer than the 20-second cycle recorded in testing.
The gap resulted from several real-world constraints, including satellite revisit times, communications bandwidth losses, enemy electronic interference, declining AI recognition accuracy and the need for human verification.
AI also revealed weaknesses in combat. Its ability to identify unfamiliar battlefield targets declined, while the opacity of its algorithms created a crisis of confidence in AI-assisted decisions. The system was also vulnerable to deception through adversarial attacks.
The report concludes that JADC2 has so far achieved only limited operational capability. Full operational capability is estimated to remain five to 10 years away.
It also identifies several major blind spots. JADC2 has yet to be tested in a high-intensity Indo-Pacific anti-access/area-denial conflict. Compatibility with the nuclear command, control and communications system remains unresolved. Interoperability with the many allies outside the Five Eyes intelligence community also remains largely conceptual.
4. Multiple Risks That Cannot Be Avoided
1. Institutional Risk: The Services’ Own Interests Are Difficult to Overcome
Each service has its own technical road map and budgetary priorities. Because the organizations at the top lack the authority to impose common standards, the result is a large number of heterogeneous systems. Interoperability depends on additional gateways to translate between them, increasing both latency and the number of potential failure points.
Budget fragmentation compounds the problem. Because JADC2 has no independent funding line and its resources are scattered across individual service programs, Congress has difficulty conducting comprehensive oversight.
2. Vulnerabilities Built into the Technology Architecture
The system is heavily dependent on commercial cloud services and commercial low-Earth-orbit constellations. The ability of commercial providers to maintain service during a conflict has not been tested in wartime conditions.
AI algorithms are vulnerable to adversarial attacks. An opponent could deceive, jam or contaminate incoming data, resulting in false alarms and incorrect assessments.
Communications, positioning and timing rely heavily on space assets. Anti-satellite attacks and electronic interference could therefore directly disrupt the entire kill network.
The transition to post-quantum cryptography is a massive undertaking, and the system remains in the middle of a shift from legacy encryption algorithms to new ones.
3. The Dilemma of Allied Interoperability under CJADC2
Bringing allies into the operational network requires sharing data. But the more data is shared, the greater the risk of leaks.
The Mission Partner Environment faces questions of national sovereignty. Allies are reluctant to hand over their most sensitive intelligence in full. AUKUS members and the United States and Japan can achieve relatively high levels of coordination, but most NATO and Indo-Pacific partners remain limited to tactical data exchanges and cannot yet support deep operational-level integration.
5. Lessons: Do Not Simply Copy the Model. Understand Both Its Strengths and Its Weaknesses
The data-centric approach represented by JADC2 is an important direction in the evolution of future command and control. It offers several practical lessons.
First, a paradigm shift is not simply a matter of buying new equipment. The core issue is data governance. Hardware platforms can be upgraded, but common data standards, semantic metadata and data-security systems provide the foundation for cross-domain coordination. Without them, simply adding more systems will not eliminate information stovepipes.
Second, it is essential to distinguish between optimal exercise performance and degraded combat performance. Impressive kill-chain figures achieved in controlled experiments can deteriorate sharply in real combat, where electronic interference, degraded communications and target concealment are present. Capability assessments must therefore account for degraded operating conditions.
Third, advanced architectures have two sides. They can be powerful while simultaneously creating new vulnerabilities. JADC2 depends heavily on communications, space assets and commercial computing power. These are sources of capability, but they are also potential targets. Counter-command-and-control operations, anti-satellite attacks, electronic warfare and AI deception will all become important ways of countering such systems.
Fourth, institutional reform is as important as technology. Even the best technology will struggle to deliver its intended capabilities if organizational parochialism and unclear responsibilities remain. The intelligent transformation of command and control is a comprehensive undertaking involving technology, organization, personnel and institutions.